SonicWall SSL VPN flaw CVE-2026-19868 is being exploited. Learn how healthcare teams can verify exposure, coordinate the update, and test remote access.
Use this quarterly healthcare vendor access review to identify outside access, reduce unnecessary permissions, document ownership, and protect care continuity.
Use this healthcare employee offboarding checklist to remove access, preserve records, protect patient data, and maintain care continuity securely in practice.
Microsoft released its October security updates on October 13, 2026, addressing an actively exploited Windows Shell vulnerability. The vulnerability is rated High, with a CVSS score of 8.8. For healthcare organizations, the immediate priority is verifying that supported Windows devices received the applicable update. QUICK ANSWER Ask your IT provider to verify successful installation, identify failed or offline devices, complete required restarts, and document unresolved exceptions.
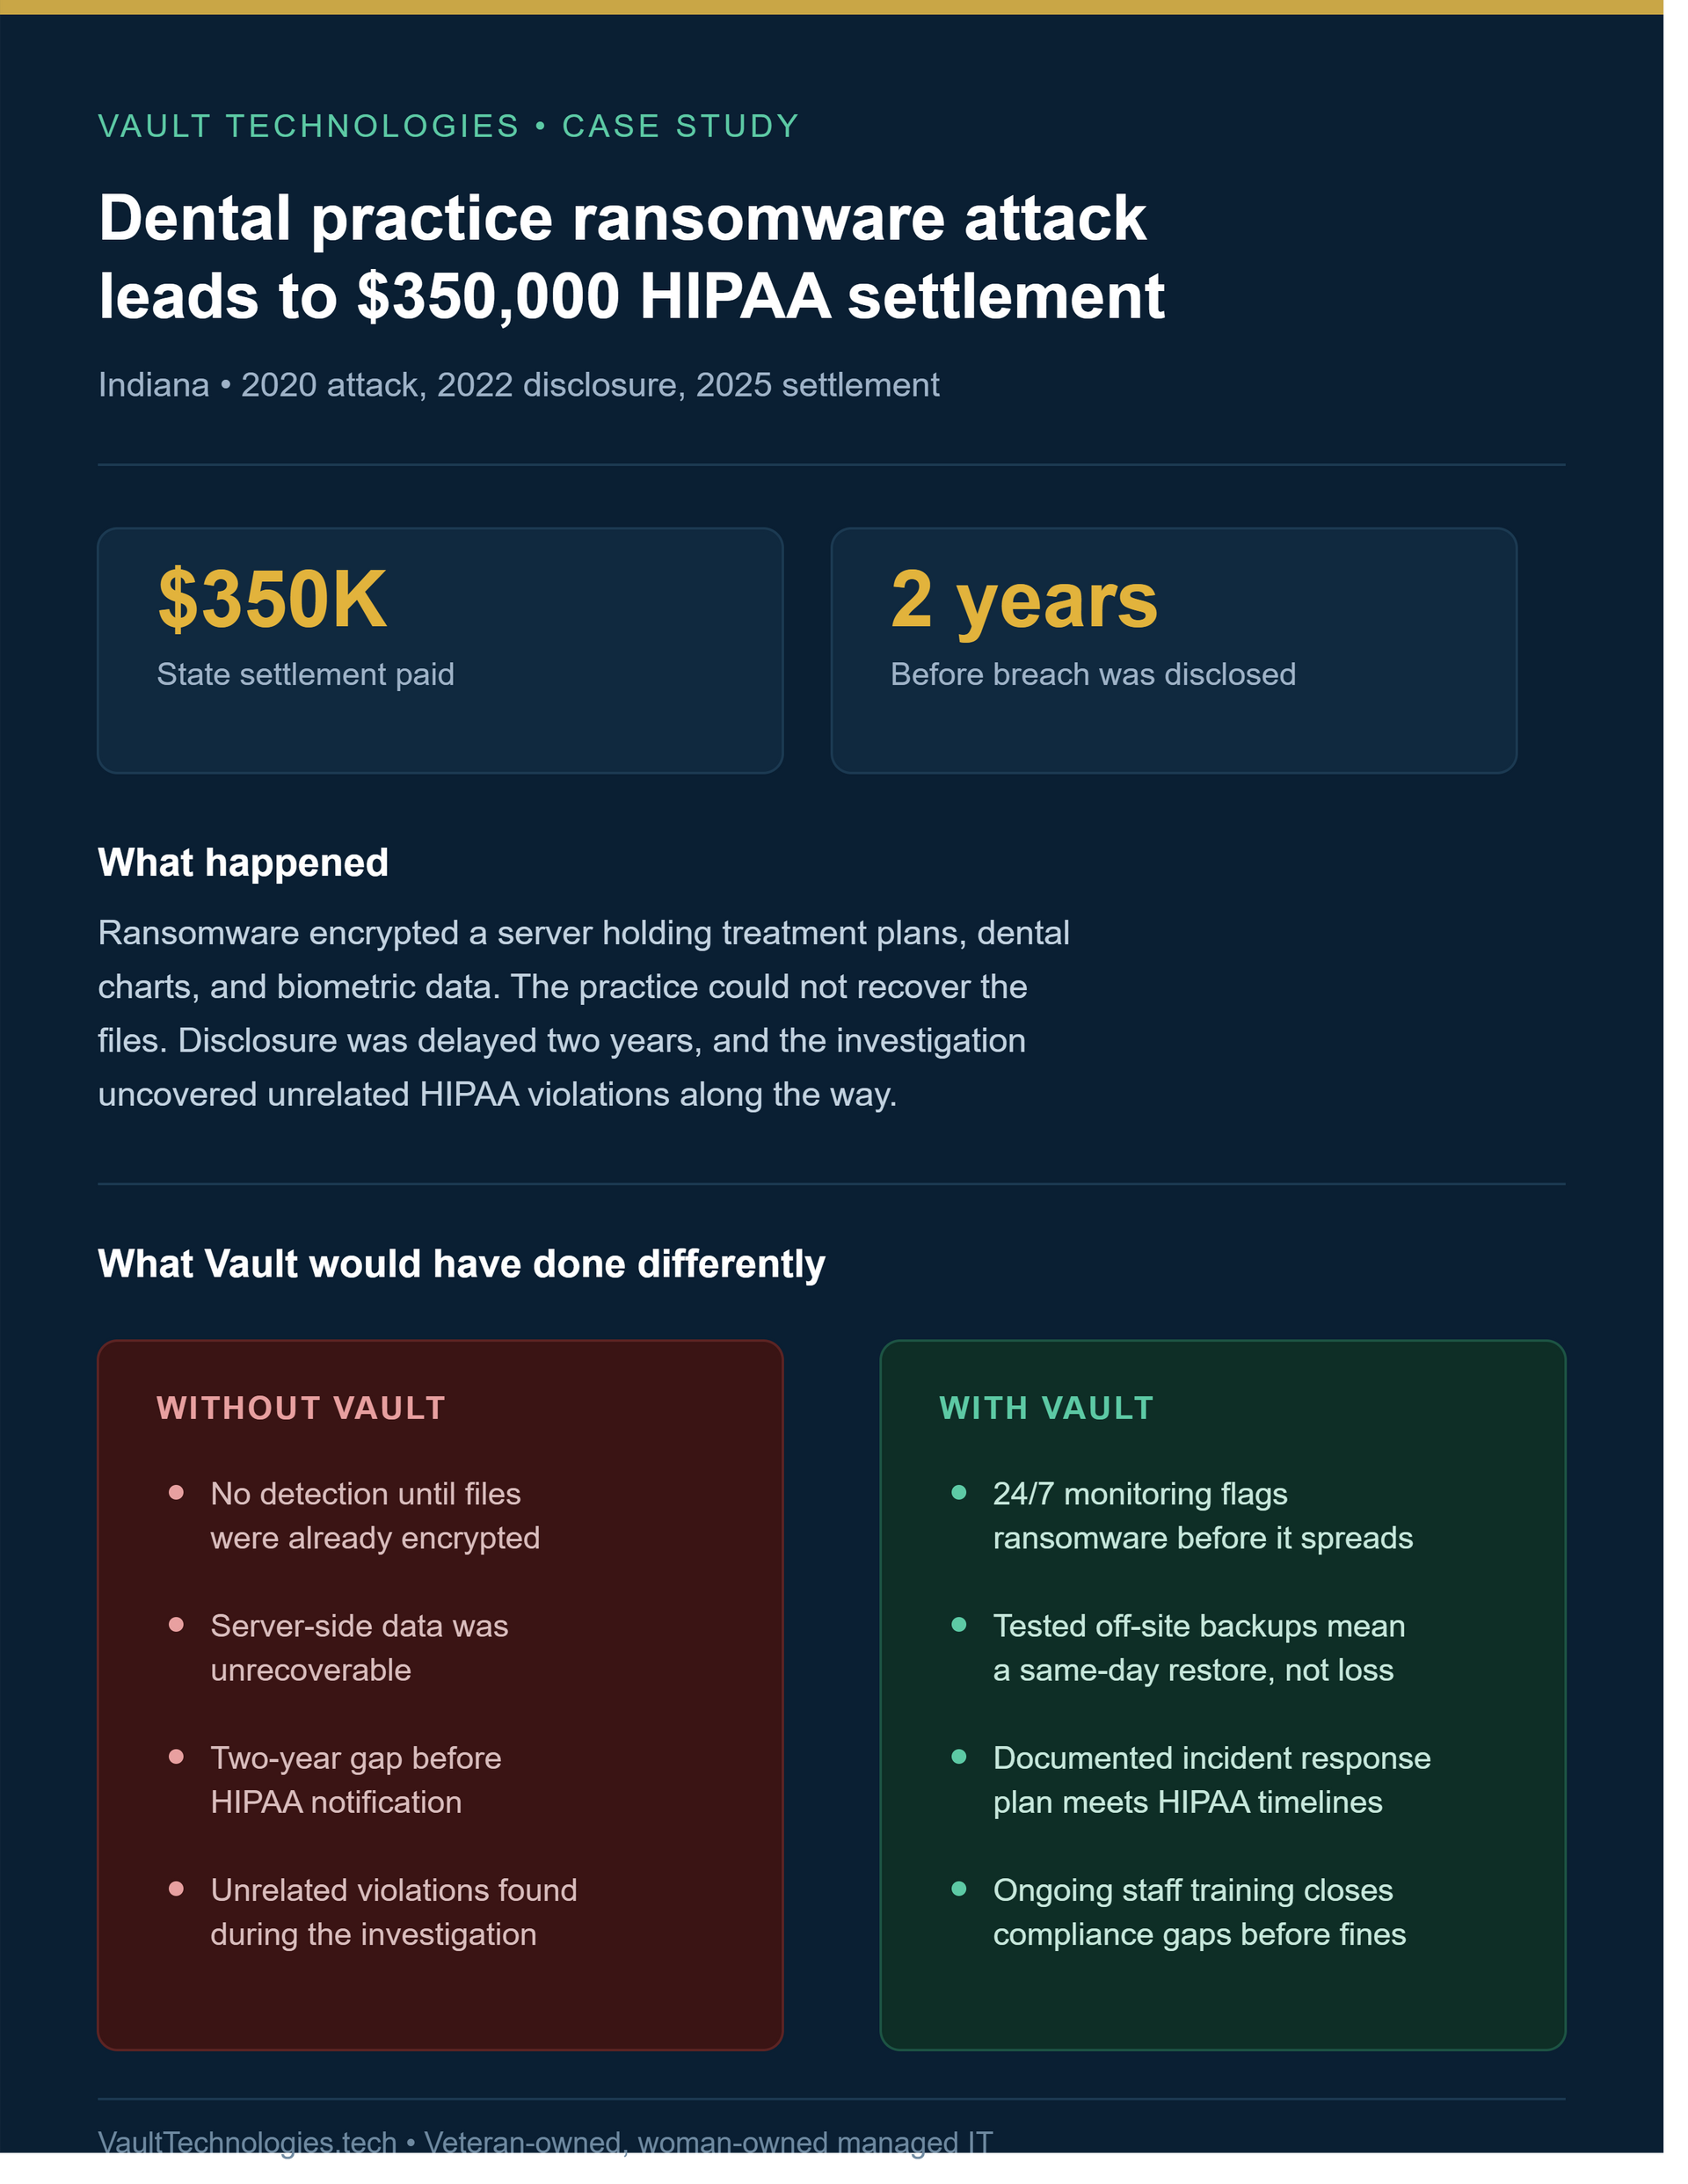
A $350,000 dental ransomware settlement shows why practices need documented incident response, tested backups, clear vendor ownership, and legal review plans.
A January 2025 ransomware attack on a Maryland medical group exposed 934,000 patient records and triggered class-action lawsuits. See what proactive IT management would have changed.
See how Vault Technologies combines healthcare IT, cybersecurity, clinical insight, and care-continuity planning for Oregon healthcare organizations and practices.
Use this 12-record healthcare IT documentation checklist to organize systems, vendors, user access, backups, downtime plans, and technology priorities safely.
When an employee leaves a healthcare organization, disabling one email account is not enough. The departing person may have access to an EHR, Microsoft 365, shared mailboxes, cloud files, clinical applications, scheduling systems, billing platforms, remote-support tools, mobile devices, door controls, vendor portals, and locally stored information. At the same time, immediately deleting every account can remove email, documents, contacts, calendars, workflow knowledge, or files another employee needs to continue patient care and business operations. Effective offboarding must accomplish two goals together: End the departing person’s access. Preserve the organization’s information and responsibilities. Quick Answer: How should a healthcare organization offboard an employee? Use a coordinated checklist owned by an authorized manager and completed by HR, IT, and relevant application owners. At the approved departure time: Disable sign-in through the authoritative identity system. Revoke active sessions and authentication tokens. Remove access from the EHR and other applications that do not deactivate automatically. Recover or secure organization-owned devices, badges, keys, and authentication methods. Preserve and transfer business records before deleting accounts or licenses. Redirect necessary communications to an approved employee or shared mailbox. Document every completed action, exception, owner, and timestamp. Verify that access is actually unavailable. Microsoft explains that disabling a user does not necessarily end every active application session immediately. Applications can maintain their own session tokens, and those sessions may require separate deprovisioning. Why healthcare offboarding is more than an HR task A departure changes several kinds of access at once. Identity access This includes: Microsoft 365 Microsoft Entra ID Active Directory Workstation sign-in VPN access Remote desktop Password-management systems Multifactor-authentication methods Single sign-on Administrative accounts Clinical and operational access This may include: EHR and practice-management systems Electronic prescribing Clinical messaging Laboratory and imaging portals Pharmacy platforms Scheduling systems Telehealth and remote-patient-monitoring tools Billing and claims systems Medical-device portals Hospice or home-health applications Resident or care-management platforms Physical access This may include: Building keys Access cards Alarm codes Medication-area access Server or network closets Records rooms Organization vehicles Storage areas Information ownership The departing employee may control or possess: Email conversations Patient-service communications Calendars OneDrive files Shared documents Vendor contacts Procedures and checklists Device passcodes Project files Records stored outside approved shared locations A reliable process must address all four areas. What does HIPAA say about terminating access? The HIPAA Security Rule requires regulated organizations to maintain policies and procedures so workforce members have access appropriate to their roles. HHS’s audit protocol specifically addresses procedures for terminating access to electronic protected health information when employment or another workforce arrangement ends. It also examines access-control devices, contractors, role changes, termination timeframes, exit procedures, and documentation showing that access was removed in a timely manner. The exact safeguards appropriate for an organization depend on its size, structure, systems, risks, and circumstances. HHS describes the Security Rule as flexible, scalable, and technology-neutral. This article provides operational guidance, not a legal conclusion or compliance certification. Start before the employee’s final day Good offboarding begins during onboarding. An organization cannot reliably remove access it never documented. Each workforce member should have an access record showing: Legal name and preferred name Job title and department Manager Work location Start date Organization-owned devices Primary identity account Email addresses and aliases EHR role Application access Shared mailboxes Shared drives and cloud libraries Security groups Distribution lists Vendor portals Administrative privileges Mobile-device enrollment MFA methods Physical-access items Access approvals Training status This record should be updated when the person changes roles, locations, departments, or responsibilities. Planned and urgent departures require different timing Planned departure A resignation, retirement, contract completion, or scheduled transfer allows time to: Identify responsibilities that need reassignment Move files into approved shared locations Transfer vendor relationships Review shared mailboxes and calendars Document recurring work Recover equipment Schedule access removal Prepare an internal communication plan The employee should not be asked to share passwords. Access should be transferred through administrative controls. Immediate or high-risk departure An involuntary termination, suspected account compromise, policy violation, or credible insider-risk concern may require access to be removed before or during the separation meeting. Coordinate the exact timing among authorized leadership, HR, IT, security, and legal or compliance resources as appropriate. Do not place termination details, allegations, medical information, or unnecessary personal information into an ordinary help-desk ticket. Record only what authorized technical personnel need to perform the approved actions. The healthcare employee-offboarding process Step 1: Establish the authorized request The request should identify: Employee or contractor Manager Last working date Exact access-removal time Planned or immediate departure Systems known to be used Equipment assigned Business records requiring transfer Approved mailbox or communication handling Authorized decision-maker Special legal, compliance, or safety instructions IT should not guess whether a departure is voluntary, immediate, or delayed. A specific cutoff time is safer than “sometime Friday.” Step 2: Identify the authoritative identity source Determine where the user account originates. Common configurations include: Microsoft Entra ID only On-premises Active Directory only Active Directory synchronized to Microsoft Entra ID A separate identity provider Independent accounts in each application In a synchronized environment, disabling an account in the wrong location may be ineffective or later overwritten. Microsoft advises organizations with synchronized identities to Step 3: Block sign-in and revoke sessions For Microsoft environments, the required actions may include: Disable the user in Active Directory or Microsoft Entra ID. Block new sign-ins. Revoke active sessions and refresh tokens. Disable or secure registered devices. Review authentication methods. Remove privileged roles. Remove application assignments. Remove group memberships where appropriate. Review recent sign-in activity when the circumstances justify it. Revoking sessions matters because an employee may already be signed in on a browser, mobile application, or workstation. Microsoft notes that applications can issue and control their own session cookies. Disabling the Entra account may not directly terminate a session maintained by another application. Step 4: Disable independent application accounts Not every healthcare application uses Microsoft Entra ID or Active Directory. Review the access list and disable the user directly in: EHR and practice-management systems Electronic-prescribing services Clinical messaging Laboratory and imaging portals Billing and clearinghouse platforms Telehealth systems Scheduling applications Vendor support portals Remote-access tools Backup consoles Security-camera systems Medical-device portals Password managers Cloud-storage services Website administration Social-media and marketing systems For each system, record: Action taken Date and time Administrator Account status Sessions terminated Access reassigned Exceptions Verification result Step 5: Address shared credentials safely Shared credentials make offboarding more difficult because the organization may not know who still possesses the password. When shared credentials cannot yet be eliminated: Change the password. Update approved password-management records. Revoke active sessions where possible. Replace shared MFA destinations. Review recovery email addresses and phone numbers. Notify only authorized users of the new access method. Record why the shared account still exists. Create a plan to replace it with named accounts. Do not email or text a new shared password to a large group. Step 6: Secure devices and locally stored information Identify every organization-owned or organization-managed device assigned to the person: Desktop Laptop Tablet Smartphone External drive USB storage Security token Smart card Printer or scanner storage Home-health or field device Medical device with local user access Record the asset tag, serial number, condition, return date, and responsible custodian. Before wiping or reassigning a device: Confirm that necessary files have been preserved. Confirm whether a legal or investigative hold applies. Check for locally stored business information. Remove the former user’s access. Validate encryption and device-management status. Follow the organization’s approved reset and redeployment process. Microsoft notes that a remote wipe requires the device to connect to the internet; an offline device may retain locally stored information until the command can run. Wiping also makes device data unrecoverable, so preservation decisions must come first. Step 7: Preserve email and cloud files before deletion Disabling access and deleting an account are separate decisions. Microsoft’s former-employee workflow recommends considering: Preserving mailbox contents Wiping or blocking mobile devices Forwarding necessary email Converting the mailbox to a shared mailbox where appropriate Assigning access to Outlook and OneDrive information Removing licenses Deleting the account only after required information has been handled Microsoft reports that deleting an account ordinarily begins a limited restoration period, but retention behavior depends on the account, licensing, configuration, workload, and applicable retention policies. Before deleting anything, determine: Who owns the business information? Who needs continuing access? Which records must be retained? Is a legal, compliance, or investigation hold required? Should email be forwarded? Should the mailbox become a shared mailbox? Where should OneDrive documents be moved? Are patient-care or billing tasks still pending? Are personal files mixed with organizational records? When will the account become eligible for deletion? Avoid relying on a temporary default-recovery period as the organization’s retention plan. Step 8: Reassign responsibilities Access removal is only half the process. Work must also continue. Reassign: Patient callbacks Referral coordination Prior authorizations Billing follow-up Vendor communication Shared calendars Scheduled reports Recurring meetings Equipment maintenance Domain or certificate renewals Subscription ownership Purchasing approvals Documentation ownership Emergency contacts After-hours duties Confirm that the replacement employee has appropriate access based on their role. Do not copy every permission from the departing employee without review. Step 9: Recover physical access Collect or deactivate: Building keys Access cards Alarm credentials Office keys Records-room access Server-room access Parking or gate credentials Organization identification Physical security tokens Organization payment cards If a shared physical code was known to the departing person, determine whether it must be changed. Step 10: Verify the result The technician who completed the checklist should verify that: The former user cannot sign in. Active sessions were addressed. EHR and clinical-system accounts are inactive. Administrative roles were removed. Remote access is unavailable. Mobile-device actions are complete or pending. Email and files are assigned correctly. Equipment is returned or listed as outstanding. Physical access is removed. Exceptions have owners and deadlines. Completion evidence is retained. For higher-risk departures, consider having a second authorized person review the completed checklist. Why deleting the Microsoft 365 license first can cause problems License removal may appear to be the fastest way to stop access, but it should not be the first or only step. Removing a license does not replace: Blocking sign-in Revoking sessions Disabling other applications Preserving email Moving OneDrive files Reviewing shared mailboxes Securing devices Removing physical access Documenting completion It may also change how email, files, applications, and retention features behave. The safer sequence is generally: Disable access. Revoke sessions. Preserve and transfer required information. Reassign communications and responsibilities. Remove licenses when appropriate. Delete the account only after retention and operational requirements are resolved. The exact sequence should reflect the organization’s Microsoft configuration and approved policy. Common offboarding failures HR tells IT too late If IT learns about the departure after the employee has left, accounts and sessions may remain available longer than intended. Correction: Require a standard request with an exact cutoff time. The Microsoft account is disabled, but the EHR remains active Independent healthcare applications may not receive identity changes automatically. Correction: Maintain an application-access list and assign an owner to each system. The account is deleted before records are transferred Email, files, contacts, calendars, or workflow history can become difficult to recover. Correction: Separate immediate access removal from later account deletion. Shared passwords are not changed A former employee may retain access to a shared portal even after their named accounts are disabled. Correction: Replace shared accounts where possible; otherwise rotate credentials and authentication methods. The employee’s mobile device remains connected Email, documents, messages, or application data may remain available through cached sessions or locally stored data. Correction: Use approved device-management and application-protection controls, and verify their status. No one takes ownership of ongoing work Patient callbacks, referrals, billing questions, or vendor renewals may be missed. Correction: Include operational reassignment in the offboarding checklist. Contractors are excluded Temporary staff, consultants, students, volunteers, agency personnel, vendors, and former owners may possess sensitive access. Correction: Apply the process whenever any workforce or business arrangement ends—not only when a payroll employee leaves. Why this matters to healthcare organizations Independent medical and dental practices One employee may manage scheduling, billing, vendor communication, and shared mailboxes. Deleting that account without transferring information can disrupt several workflows simultaneously. A short, repeatable checklist is more reliable than depending on one office manager’s memory. Hospice and home-health providers Remote staff may use mobile devices, home networks, cloud applications, and locally cached information. Offboarding must account for equipment return, remote sessions, mobile applications, and documentation needed by continuing care teams. Assisted-living and senior-living organizations Departing staff may have access to resident records, medication-related systems, scheduling, communications, door controls, and shared nursing-station devices. Clinical and physical access should be coordinated. Outpatient clinics EHR access is only one part of the environment. Laboratory, imaging, referral, prescribing, billing, and patient-communication portals may each require separate action. Small organizations using outside IT providers Leadership must communicate departures to the IT provider early enough to coordinate access removal. The organization should receive written confirmation showing which systems were addressed and which actions remain pending. Protect / Operate / Recover / Grow Protect Give each workforce member a named account. Require MFA where supported. Limit access according to job responsibilities. Separate ordinary and administrative accounts. Record assigned devices and applications. Eliminate unnecessary shared credentials. Review recovery emails, phone numbers, and authentication methods. Define urgent and routine departure procedures. Operate Maintain one access list for each workforce member. Require an authorized offboarding request. Include contractors, temporary staff, students, volunteers, and vendors. Coordinate HR, management, application owners, and IT. Use an exact access-removal time. Separate access suspension from account deletion. Record completion evidence and exceptions. Test the process with a tabletop exercise. Recover Preserve required email, files, and operational records. Maintain an approved method for restoring mistakenly deleted accounts or data. Document mailbox and OneDrive ownership. Escalate missing devices or unexpected access. Review sign-in activity when circumstances warrant it. Preserve relevant logs and records during an investigation. Confirm that patient-service responsibilities were reassigned. Grow Automate provisioning and deprovisioning where practical. Connect approved applications to centralized identity management. Reduce manually maintained accounts. Review access when employees change roles. Track offboarding completion time. Review recurring exceptions. Include access removal in vendor and contract requirements. Update the process when new systems are adopted. Microsoft recommends automated deprovisioning where possible and a documented manual process for applications that cannot be deactivated automatically. A simple offboarding record For each departure, retain: Person’s name Employment or relationship type Manager Approved cutoff date and time Request authorization Identity system disabled Sessions revoked EHR access removed Other applications removed Administrative privileges removed MFA methods addressed Device status Email disposition File disposition Physical-access status Responsibilities reassigned Exceptions Exception owners and deadlines Technician Completion date and time Reviewer, when required Do not place unnecessary private employment details in the technical record. The bottom line Healthcare employee offboarding is successful when the former worker can no longer access organizational systems, while the organization retains the information and operational continuity it still needs. The essential sequence is: Authorize. Disable. Revoke. Preserve. Transfer. Verify. Document. Do not confuse disabling an account with completing the entire process—and do not confuse deleting an account with securing it. Frequently asked questions When should a departing healthcare employee’s access be removed? Remove access at the time authorized by leadership, HR, or the organization’s approved procedure. Immediate or high-risk departures may require coordinated removal before or during the separation meeting. Planned departures should still have an exact cutoff time. Is disabling a Microsoft 365 account enough? No. Active sessions, independent applications, EHR accounts, mobile devices, shared credentials, physical access, and locally stored information may require separate action. Should the former employee’s account be deleted immediately? Usually not before required email, files, contacts, calendars, and business records are preserved or transferred. Immediate sign-in blocking and eventual account deletion are different actions. What happens to a former employee’s email? The organization may preserve the mailbox, grant authorized access, forward necessary messages, or convert it to a shared mailbox, depending on operational, privacy, legal, licensing, and retention requirements. Does changing the employee’s password end every session? Not necessarily. Tokens, application sessions, mobile applications, and independently managed systems may continue to operate. Administrators should disable access and revoke sessions using the appropriate identity and application controls. Does the process apply to contractors and temporary workers? Yes. Anyone with organizational access should have that access reviewed and removed when their employment, contract, placement, volunteer role, student rotation, or vendor relationship ends. How can a small healthcare practice manage offboarding without a large IT department? Use a short checklist, maintain an employee-access list, assign an owner to every application, notify the IT provider in advance, and require written completion confirmation. The process matters more than the organization’s size. Strengthen your access-management process Vault Technologies helps healthcare organizations document user access, coordinate Microsoft 365 and endpoint administration, improve onboarding and offboarding, reduce shared-account dependence, and create practical procedures that support both security and care continuity. Our nurse-led perspective helps keep technical decisions connected to patient workflows, staffing transitions, and reliable operations. Our veteran-owned team emphasizes accountability, clear documentation, and security-first support. A complimentary Technology Health Assessment can help identify gaps across identity management, endpoints, vendor access, documentation, backup planning, and continuity readiness. The assessment is a planning tool. It is not a legal opinion, compliance certification, penetration test, forensic investigation, or guarantee against a security incident. Authoritative sources HHS Office for Civil Rights — HIPAA Audit Protocol , updated July 2018. The workforce-security section addresses access authorization, role changes, termination procedures, access-control devices, contractors, and documentation. HHS.gov HHS — Summary of the HIPAA Security Rule , current version reviewed October 5, 2026. HHS.gov Microsoft Learn — Revoke User Access in Microsoft Entra ID , updated June 19, 2026. Microsoft Learn Microsoft Learn — Remove a Former Employee and Secure Data , updated June 15, 2026. Microsoft Learn CISA and NSA — Identity and Access Management Recommended Best Practices for Administrators , published March 2023.
An actively exploited ScreenConnect flaw affects remote-support clients. Learn what healthcare organizations should verify with their IT providers now.